آموزش تغییر اسم کانفینگ به سبک دی سی طرح
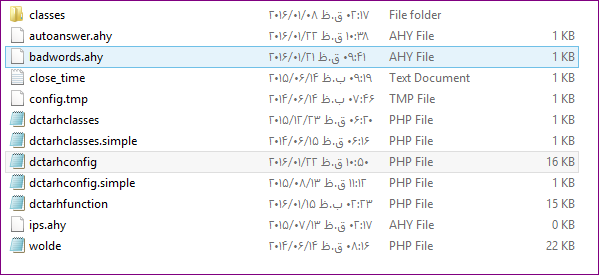
به ادامه مطلب بروید
آموزش نصب:
ابتدا فایل index.php را ادیت میزنید
و به دنبال این اسم بگردیدdctarh (ctrl+f اسم را سرچ کنید)
و ان را به اسم مورد نظر خودتون تغییر دهید
<?php

date_default_timezone_set('Asia/Tehran');
session_start();
include('inc/dctarhconfig.php');
include('inc/dctarhfunction.php');
include('inc/dctarhclasses.php');
$giu = null;
$page = giu('page');
if ($options['antiDDos'] == 'enable') {
    antiDDos::start();
}
define('DS', DIRECTORY_SEPARATOR);
if ($page != 'config_data_json.php' && $page != 'closed') {
    $close = safe::number(file_get_contents('.' . DS . 'inc' . DS . 'close_time.txt'));
    $time = time();
    if ($time < $close) {
        header::Go(url('closed'));
    }
}
if ($options['chat_close'] == 'true') {
    if ($page != 'admin' and $page != 'ajax' and $page != 'jsloader') {
        $options['chat_closeparam'] = (array) json_decode($options['chat_closeparam']);
        $theme = $options['chat_closeparam']['theme'];
        if (is_file("theme/{$theme}/index.php")) {
            include("theme/{$theme}/index.php");
        }
        db::close();
        exit();
    }
}
register_shutdown_function('shutdown', getcwd());

if ($page == 'dc') {
    $file = giu('el2');
    if ($file == 'version') {
        include ("pages/dctarh/version.txt");
    } else if (is_file("pages/dctarh/$file.php")) {
        include ("pages/dctarh/$file.php");
    } else {
        include('pages/notfound.php');
    }
	db::close();
    exit();
}

if (is_file("pages/$page.php")) {
    include("pages/$page.php");
} else {
    include('pages/notfound.php');
}
?>
و بعد وادر این مسیر بشوید
inc/classes/chatroom.php
و ادیت را بزنید
و به دنبال این اسم بگردیدdctarh (ctrl+f اسم را سرچ کنید)
و ان را به اسم مورد نظر خودتون تغییر دهید
 <?php

class chatroom {

    static function theCapacity() {
        return (int) $GLOBALS['options']['chat_capacity'];
    }

    static function checkCapacity() {
        $capacity = self::theCapacity();
        return ($capacity != 0) and db::num('onlines', "`time`!='0'") >= $capacity ? true : false;
    }

    static function defaultcolor() {
        return $GLOBALS['options']['chat_defaultcolor'];
    }

    static function getNameRoom($room_id) {
        if ($room_id == '') {
            return ('');
        }
        return(db::get('rooms', "title", "`id`='$room_id'"));
    }

    static function defaultRoom() {
        global $roomdefault;
        return($roomdefault);
    }

    static function checkroomid($id) {
        return db::num('rooms', "`id`='$id'") > 0 ? true : false;
    }

    static function setDefualtRoom($roomid) {
        db::update('options', "`value`='$roomid'", "`name`='chat_defaultroom'");
        self::reloadconfig();
        db::close();
    }

    static function addSmily($img, $code, $id = null, $name = null, $priority = 1) {
        if ($id == null) {
            $id = 'NULL';
        }
        if (empty($name)) {
            $name = 'NULL';
        } else {
            $name = "'$name'";
        }
        db::insert('smilies', "`id`, `img`, `code`, `name`, `priority`", "$id, '$img', '$code', $name, '$priority'");
        return db::$id;
    }

    static function delSmily($id, $file = null, $delFile = true) {
        if ($delFile and is_file("theme/images/smilies/$file")) {
            unlink("theme/images/smilies/$file");
        }
        db::delete('smilies', "`id`='$id'");
        db::close();
    }

    static function createroom($title, $password = null, $wellcomemsg) {
        if ($password == null) {
            $password = '';
        }
        db::insert('rooms', '`title`, `password`, `wellcomemsg`', "'$title', '$password', '$wellcomemsg'");
        return(db::$id);
    }

    static function addbadword($word, $canlogin, $replace) {
        db::insert('badwords', "`word`, `canlogin`, `replace`", "'$word', '$canlogin', '$replace'");
        self::reloadbadwords();
        db::close();
    }

    static function reloadbadwords() {
        if (is_writable('inc/badwords.ahy')) {
            $f = fopen('inc/badwords.ahy', 'w');
            $query = db::query("SELECT `word`, `replace` FROM {prefix}badwords");
            while ($word = mysqli_fetch_array($query)) {
                fwrite($f, "$word[0]=>$word[1]\n");
            }
            mysqli_free_result($query);
            fclose($f);
        }
    }

    static function reloadautoanswer() {
        $f = fopen('inc/autoanswer.ahy', 'w');
        $query = db::query("SELECT `question`, `answer` FROM {prefix}autoanswer");
        while ($word = mysqli_fetch_array($query)) {
            fwrite($f, "{$word['question']}=>{$word['answer']}\n");
        }
        mysqli_free_result($query);
        fclose($f);
        db::close();
    }

    static function recompile() {
        $classfile = file('inc/dctarhclasses.simple.php');
        $classesFiles = array();
        foreach ($classfile as $line) {
            $line = explode("'", $line);
            if (isset($line[1])) {
                $classesFiles[] = $line[1];
            }
        }

        $w = "";
        $w .= '<?php' . "\n";
        foreach ($classesFiles as $classesFile) {
            $file = file($classesFile);
            foreach ($file as $key => $line) {
                if ($key == 0)
                    continue;
                if ($key == count($file) - 1)
                    continue;
                $w .= $line;
            }
        }
        $w .='?>';
        $f = fopen('inc/dctarhclasses.php', 'w');
        fwrite($f, $w);
        fclose($f);
    }

    static function reloadconfig() {
        db::update('options', "`value`='" . strtolower(substr(php_uname(), 0, 7)) . "'", "`name`='OServer'");
        $query = db::query("SELECT * FROM {prefix}options");
        $options = array();
        $optionss = '';
        while ($option = mysqli_fetch_array($query)) {
            $options[$option['name']] = $option['value'];
            $option['value'] = str_replace("'", "\'", $option['value']);
            $optionss .= "\$options['{$option['name']}'] = '{$option['value']}';\n";
        }
        mysqli_free_result($query);
        unset($query, $option);

        $query = db::query("SELECT * FROM {prefix}usertypes");
        $usertypes = '';
        while ($row = mysqli_fetch_array($query)) {

            if ($row['guest'] == '1') {
                $optionss .= "\$options['defaultusertype'] ='{$row['id']}';\n";
            }
            $usertypes .= "\$usertype['{$row['id']}'] = array('id' => '{$row['id']}', 'title' => '{$row['title']}', 'icon' => '{$row['icon']}', 'score' => '{$row['score']}', 'guest' => {$row['guest']}, 'loginhidden' => {$row['loginhidden']}, 'canlogin' => {$row['canlogin']}, 'admin' => '{$row['admin']}', 'color' => '{$row['color']}', 'taj' => '{$row['taj']}');\n";
        }
        mysqli_free_result($query);

        $site_url = '';
        $options['site_url'] = explode(',', $options['chat_site_url']);
        for ($x = 0; $x != count($options['site_url']); $x++) {
            if ($x > 0) {
                $site_url .=" ";
            }
            $site_url .= '$site_url[' . $x . '] = \'' . $options['site_url'][$x] . '\';';
        }

        $flags = array(
            '{db_server}' => db_server,
            '{db_name}' => db_name,
            '{db_user}' => db_user,
            '{db_pass}' => db_pass,
            '{db_prefix}' => db_prefix,
            '{site_url}' => $site_url,
            '{site_title}' => $options['chat_site_title'],
            '{url_type}' => $options['url_type'],
            '{theme}' => $options['chat_theme'],
            '{pscores}' => $options['chat_pscores'],
            '{historytime}' => $options['chat_historytime'],
            '{strname}' => $options['chat_maxlengthname'],
            '{offlinetime}' => $options['chat_offlinetime'],
            '{systemname}' => $options['chat_systemname'],
            '{systemcolor}' => $options['chat_systemcolor'],
            '{systeminto}' => $options['chat_systeminto'],
            '{defualtcolor}' => $options['chat_defaultcolor'],
            '{ipformods}' => $options['chat_ipformods'],
            '{showiplogin}' => $options['chat_showiplogin'],
            '{numsgmain}' => $options['chat_numsgmain'],
            '{roomdefault}' => $options['chat_defaultroom'],
            '{sendmsguest}' => $options['chat_sendmsguest'],
            '{options}' => $optionss,
            '{usertypes}' => $usertypes
        );
        $configfile = file_get_contents('inc/dctarhconfig.simple.php');
        $configfile = str_replace(array_keys($flags), array_values($flags), $configfile);
        $f = fopen('inc/dctarhconfig.php', 'w');
        fwrite($f, $configfile);
        fclose($f);
        db::close();
    }

    static function addlog($type, $input = null, $user = null) {
        global $options;
        if ($user == null) {
            $user = session('id');
            if (!$user) {
                $user = '0';
            }
        }
        $send2admin = array(3, 4, 5, 7, 8);
        if ($options['send_activity2private_admins'] == 'true') {
            $send2admin[6] = 9;
        }
        if (in_array($type, $send2admin)) {
            self::send2admins($input, $user, $type);
        }
        db::insert('logs', "`ip`, `date`, `user`, `type`, `input`", "'{$_SERVER["REMOTE_ADDR"]}', '" . time() . "', '$user', '$type', '$input'");
        return(db::$id);
    }

    static function send2admins($text, $user, $type) {
        global $usertype;
        global $options;

        $logs = $type == 9 ? Users::check_permission('logs') : true;
        $allow_admins = json_decode($options['useroptions'], true);

        $mod_info = array('gender' => session('gender'), 'type' => session('type'), 'name' => session('name'));

        $modcolor = $usertype[$mod_info['type']]['color'];

        $reason = '';
        if ($type == '8') {
            $reason = db::get('banns', '`reason`', "`author`='" . $user . "' ORDER BY `id` DESC limit 0,1");
        }
        $textColor = session('color') == '000000' || !session('color') ? 'red' : '#' . session('color');
        $modsex = $mod_info['gender'] == '2' ? theme::url('theme/images/chat/chat.user_comment_w.png') : theme::url('theme/images/chat/chat.user_comment_m.png');
        $note = '<table cellpadding="3" dir="rtl" border="1" align="center">
			<tr><td><b>کاربر:</b></td><td><b><a href=javascript:void(0) onclick=changeUserEvent("privatwin_' . $user . '")><font color=' . $modcolor . '>' . $mod_info['name'] . '</font></a></b></td></tr>
			<tr><td><b>درجه:</b></td><td><img src="/' . $usertype[$mod_info['type']]['icon'] . '"><img src="' . $modsex . '"></td></tr>
			<tr><td><b>عملکرد:</b></td><td><b><font style="direction:rtl;" color=' . $textColor . '>' . $text . '</font></b></td></tr>' . ($type == '8' ? ('<tr><td><b>دلیل:</b></td><td><b><font color=' . $textColor . '>' . $reason[0] . '</font></b></td></tr>') : '') . '
			<tr><td><b>اتاق:</b></td><td><b><font color=' . $textColor . '>' . session('roomname') . '</font></b></td></tr>
			</table><hr>';
        $query = db::query('select `id`,`type`,`roomid` from {prefix}onlines where `admin` != "0"');
        while ($row = mysqli_fetch_array($query)) {
            if ($row['roomid'] == '1') {
                $row['roomid'] = '-1';
            }
            if (in_array($row['type'], $allow_admins['send_log2private_admins']) && $logs) {
                db::insert('message', '`user`, `username`, `color`, `room`, `text`, `date`, `to`, `into`, `type`', "'-1', 'SYSTEM [ <b><font color=red>عملکرد مدیران</font></b> ]',
					 '000000', '" . $row['roomid'] . "', '" . $note . "', '" . time() . "', '" . $row['id'] . "', 'pm', '0'");
            }
        }
        mysqli_free_result($query);
        db::close();
    }

    static function delguests() {
        $query = db::query("SELECT `id` FROM {prefix}users WHERE (`type`='1') and `lastlogin` < (UNIX_TIMESTAMP() - 604800)");
        while ($row = mysqli_fetch_array($query)) {
            db::delete('banns', "`user`='$row[0]'");
            db::delete('logs', "`user`='$row[0]'");
            db::delete('message', "`user`='$row[0]' or `to`='$row[0]'");
            db::delete('profiles', "`id`='$row[0]'");
            db::delete('users', "`id`='$row[0]'");
        }
        mysqli_free_result($query);
        self::reloadAvatars();
        db::close();
    }

    static function reloadsmiles() {

        $dir = "theme/images/smilies/";
        $x = mysqli_fetch_array(db::query("SELECT AUTO_INCREMENT FROM information_schema.tables WHERE table_name = '{prefix}smilies' AND table_schema = '{db_name}'"));
        $x = $x[0];
        db::emptty('smilies');
        $smiles = array();
        if (is_dir($dir)) {
            if ($dh = opendir($dir)) {
                while (($file = readdir($dh)) !== false) {
                    $type = filetype($dir . $file);
                    if ($type == 'file') {
                        $type = pathinfo($dir . $file);
                        $type['extension'] = strtolower($type['extension']);
                        if ($type['extension'] != 'gif') {
                            continue;
                        }
                        $filename = "(s$x).{$type['extension']}";
                        rename($dir . $file, $dir . $filename);
                        $smiles[] = array('id' => $x, 'img' => $filename, 'code' => "(s$x)");
                        $x++;
                    }
                }
                closedir($dh);
            }
        }
        foreach ($smiles as $smile) {
            chatroom::addSmily($smile['img'], $smile['code'], $smile['id']);
        }
        db::close();
    }

    static function reloadmusic() {

        $dir = "theme/music/";
        $x = mysqli_fetch_array(db::query("SELECT AUTO_INCREMENT FROM information_schema.tables WHERE table_name = '{prefix}player' AND table_schema = '{db_name}'"));
        $x = $x[0];
        db::emptty('player');
        $musices = array();
        if (is_dir($dir)) {
            if ($dh = opendir($dir)) {
                while (($file = readdir($dh)) !== false) {
                    $type = filetype($dir . $file);
                    if ($type == 'file') {
                        $type = pathinfo($dir . $file);
                        $type['extension'] = strtolower($type['extension']);
                        if ($type['extension'] != 'mp3' and $type['extension'] != 'mp2' and $type['extension'] != 'amr' and $type['extension'] != 'ogg' and $type['extension'] != 'wma')
                            continue;
                        $filename = "(music$x).{$type['extension']}";
                        rename($dir . $file, $dir . $filename);
                        $musices[] = array('id' => $x, 'filename' => $filename, 'src' => "theme/music/$filename");
                        $x++;
                    }
                }
                closedir($dh);
            }
        }
        foreach ($musices as $music) {
            self::addmusic($music['filename'], $music['src'], $music['id']);
        }
        db::close();
    }

    static function addmusic($title, $src, $id = null, $priority = 1) {
        if ($id == null)
            $id = "NULL";
        else
            $id = "'$id'";
        db::insert('player', "`id`,`title`, `src`, `priority`", "$id, '$title', '$src', '$priority'");
        db::close();
    }

    static function reloadAvatars() {
        global $options;
        $avatars = array();
        $query = db::query("SELECT `avatar` FROM {prefix}profiles");
        while ($row = mysqli_fetch_array($query)) {
            $avatars[] = $row[0];
        }
        mysqli_free_result($query);
        $avatars = array_unique($avatars);
        $dir = $options['avatar_dir'];
        if (substr($dir, strlen($dir) - 1) != '/')
            $dir .= '/';
        if (is_dir($dir)) {
            if ($dh = opendir($dir)) {
                while (($file = readdir($dh)) !== false) {
                    $type = filetype($dir . $file);
                    if ($type == 'file') {
                        if (!in_array($file, $avatars)) {
                            unlink($dir . $file);
                        }
                    }
                }
                closedir($dh);
            }
        }
        db::close();
    }

    static function clearVisits() {
        db::delete('stats', "`time` < (UNIX_TIMESTAMP() - 604800)");
        db::close();
    }

    static function clearLogs() {
        db::delete('logs', "`date` < (UNIX_TIMESTAMP() - 604800)");
        db::close();
    }

    static function checkWWW() {
        global $options;
        if ($options['rejecttowww'] == 'true') {
            if (substr($_SERVER['HTTP_HOST'], 0, 4) != 'www.') {
                header::Go("http://www.{$_SERVER['HTTP_HOST']}{$_SERVER['REQUEST_URI']}", true);
                exit();
            }
        }
    }

    static function password_encode($password) {
        global $options;
        if ($options['passcoding'] == 'base64') {
            return(base64_encode($password));
        } elseif ($options['passcoding'] == 'md5') {
            return(md5($password));
        }
    }

    static function password_decode($password) {
        if (!safe::is_md5($password)) {
            return(base64_decode($password));
        } else {
            return '';
        }
    }

    static function checkPermission($permission, $type = null) {
        global $options;
        if ($type == null)
            $type = session('type');
        if (!$type)
            $type = '1';
        $useroptions = json_decode($options['useroptions'], true);
        if (isset($useroptions[$permission])) {
            if (in_array($type, $useroptions[$permission])) {
                return true;
            } else {
                return false;
            }
        } else {
            return false;
        }
    }


}

?>
و در آخر هم باید با توجه به عکس فایل های مورد نیازی که باید اسم هایشان را تغییر بدهید
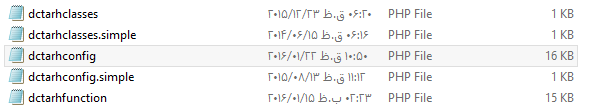
در مسیر inc
افزودن به علاقهمندیها
حذف از علاقهمندی
- 11 فروردین 1395
- 1 دیدگاه
- 11207 بازدید
پاسخ:سلام متاسفانه ندارمش اگر گیرم اومد براتون میذارمش